Recently added to KEV
CISA KEVWaiting for the CISA snapshot.
REVERSE ENGINEERING / ADVERSARIAL TESTING
A wrapped integer. A reused grant. An event wearing the wrong identity. Follow the failure in motion, then open the code and the recorded experiment behind it.
11 projects / SOURCE & EVIDENCE
01 / VISUAL ATTACK STORIES
Three attack mechanics drawn as moving systems: an integer wraps past a range check, a grant returns for a second use, and a convincing event arrives from the wrong emitter.
Attack questionAdversarial reasoning: control the input, locate the trust boundary, and trace exactly where the decision changes.
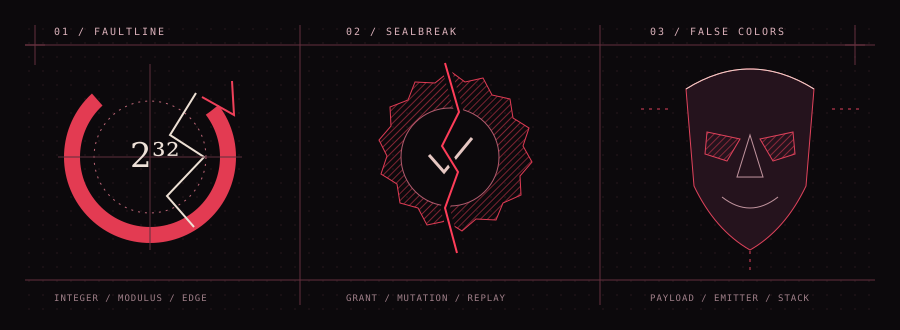
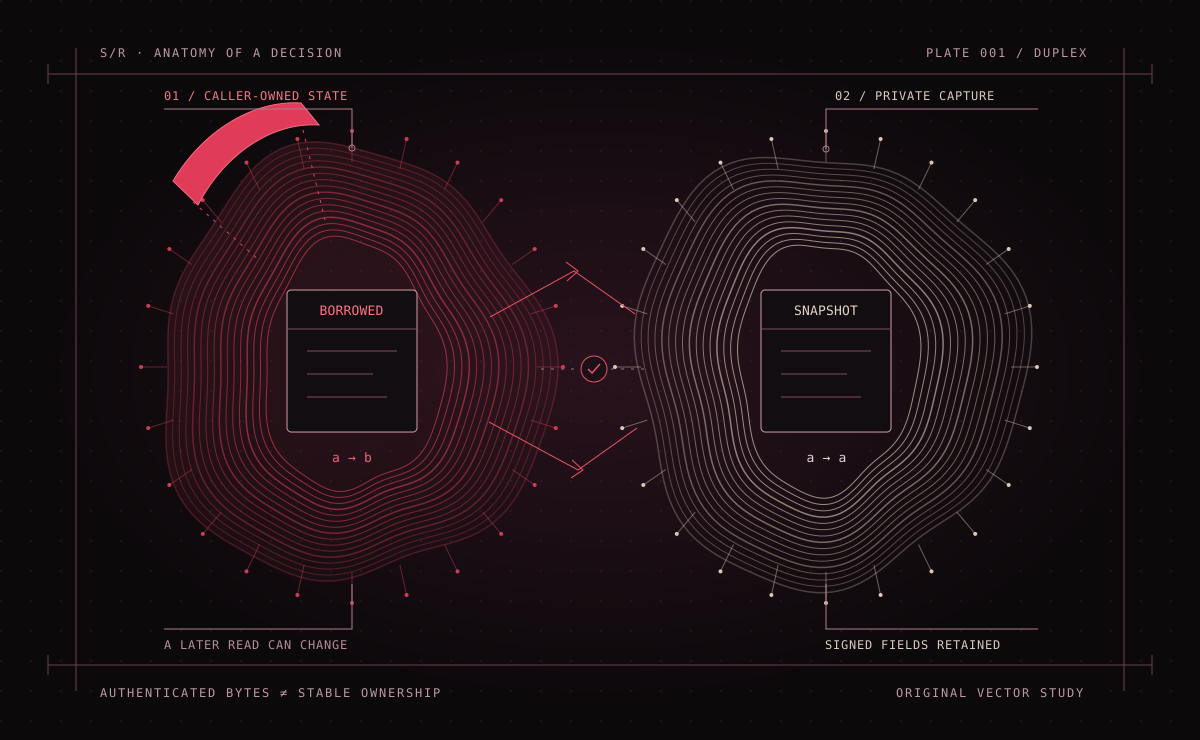
Load the scene, change the input, follow the failure.
Preview not loaded. The full page is always available.
FOLLOW THE REASONING
PUBLIC DATA / RESEARCH VIEWS
Expand a view to request its public-data snapshot.
Methods and limitations stay beside the numbers.
Public indicators returned by the existing feed service: CISA KEV, Feodo Tracker, and ThreatFox. Check the source timestamp and coverage before interpreting the sample.
Waiting for the CISA snapshot.
Waiting for the Feodo snapshot.
Waiting for the ThreatFox snapshot.
Recent NVD entries ranked by FIRST EPSS, with CVSS context and KEV membership. EPSS estimates exploitation probability over the next 30 days. A score or a missing catalog entry does not establish whether a particular system is safe.
Open this view to request the ranked snapshot.
Ranking = EPSS probability first, then CVSS severity, then recency. EPSS via FIRST.org; scores shift daily as exploitation signal accrues. This is public-data analysis, not a claim of private discovery.
This board compares a vulnerability's NVD publication date with the date CISA added it to the Known Exploited Vulnerabilities catalog: max(0, KEV dateAdded − NVD published). The interval describes time to catalog inclusion. It does not date the first exploit or measure how long a system was safe to leave unpatched. Only entries matched across the two sources are included.
Open this view to request its snapshot.
Open this view to request its snapshot.
Headlines use matched entries added to KEV from 2023 onward; the yearly chart also includes earlier additions. Historical backfills and delays in publication or cataloging affect this interval in every year. dateAdded is the catalog addition date, not the first exploitation date. Intervals at or below zero are displayed as zero; they do not establish a zero-day exploit. KEV is a selected catalog, and missing source records can reduce coverage. These figures describe catalog history and do not establish a safe patching window.
Posting counts, group activity, and sector summaries from ransomware.live. These are aggregate observations of a selected public feed, not a census of incidents or independently verified victim claims.
Open this view to request its snapshot.
Open this view to request its snapshot.
Open this view to request its snapshot.
This view presents aggregate counts. Victim names and hidden-service addresses are not displayed. The counts describe source postings and do not establish the number of confirmed breaches.
ARCHIVE / JULY–AUGUST 2026
Earlier Python projects, kept here for context.
Original repositories and methods remain available.
Concurrent discovery, service fingerprinting, and explainable finding rules. An exposed service is an observation to investigate.
Inspect source ↗Read methodology ↗ATT&CK-mapped detection rules and time-window correlation. Published fixtures and critiques make the logic reviewable.
Inspect source ↗Read critique ↗Hybrid retrieval and cited answers with a sample evaluation corpus. The critique documents decisions, corrections, and limits.
Inspect source ↗Read critique ↗These repositories precede the current studies above. The September engineering review records later local patches separately. Read that review ↗
THE PERSON BEHIND THE WORK
I’m Sergio Rodriguez, an Iona University undergraduate from New York’s Hudson Valley. I’m seeking Summer 2027 internships in security research, reverse engineering, and adversarial testing. These projects show how I form an attack hypothesis, build the smallest reproducer, and test the result against a control.
More about me ↗RECENT LEARNING
CONTINUE THE CONVERSATION